Spyke

Posts

Digital Privacy at the U.S. Border: Protecting the Data On Your Devices

The right time to start protecting your digital privacy is before your trip […] The simplest and most reliable precaution against border searches is to reduce the amount of information that you carry across the border.


Sometimes law enforcement officials achieve so-called “consent” by being vague […] You can try to dispel this ambiguity by inquiring whether border agents are asking you or ordering you […] If an agent says it is a request only, you might politely but firmly decline to comply with the request.

If you are a U.S. citizen, border agents cannot stop you from entering the country, even if you refuse to unlock your device, provide your device password, or disclose your social media information. However, agents may escalate the encounter if you refuse.

If you elect to comply with a border agent’s order to unlock your device, provide your password, or disclose your social media information, you can inform the agent that you are complying under protest and that you do not consent.


It is possible that if you unlock your device, and agents then search your device, a court will rule that you consented to the search. […] As noted in Part 1, the best way to avoid an inadvertent “consent” to search is to decline to unlock your device, provide the device password, or provide any social media information.

Technically, you don’t even need to admit that you know the password.

If you believe that border agents violated your digital rights at the border, please contact EFF at [email protected].


See also:

Digital Privacy at the U.S. Border: Protecting the Data On Your Deviceshttps://www.eff.org/wp/digital-privacy-us-border-2017Open linkView original on monero.town
24

Google addressed a new actively exploited Chrome zero-day

The fact that the issue was discovered by Google TAG suggests it was exploited by a nation-state actor or by a surveillance firm.

As usual, Google did not publish details about the attacks exploiting the flaw in the wild.

See also: https://www.cert.europa.eu/publications/security-advisories/2023-100/

This vulnerability also affects Chromium-based web browser such as Microsoft Edge [3], Brave, Opera, and Vivaldi.

Google addressed a new actively exploited Chrome zero-dayhttps://securityaffairs.com/156231/security/google-addressed-a-new-actively-exploited-chrome-zero-day.htmlOpen linkView original on monero.town
15
monero·MonerobySaki

You can now see Binance law enforcement requests for $10K in Bitcoin or Monero

“Some Hackers have figured out there is no quick and easy way for a company that receives one of these EDRs (emergency data request) to know whether it is legitimate,” he said.

“The hackers will send a fake emergency data request along with an attestation that innocent people will likely suffer greatly or die unless the requested data is provided immediately.”

You can now see Binance law enforcement requests for $10K in Bitcoin or Monerohttps://thebittimes.com/you-can-now-see-binance-law-enforcement-requests-for-10k-in-bitcoin-or-monero-tbt74181.htmlOpen linkView original on monero.town
5

Ten years from Snowden revelations – what’s next for Tor and privacy online? | Tor Project

privacy has nothing to do with having something to hide. Instead, privacy means protecting the human being that you are, all the personal details that make you, you. What you care about, what you love, what you hate, what you are curious about, what makes you laugh, what you fear. And most importantly, choosing when you decide to share that information and who you share it with.

it is possible to build technology used by millions of people with privacy at the heart. We build technology to advance that right in order to help users reclaim their agency in digital spaces.

(But by default, Tor Browser is not shipped with uBlock Origin.)

PS: ONION LINK http://pzhdfe7jraknpj2qgu5cz2u3i4deuyfwmonvzu5i3nyw4t4bmg7o5pad.onion/tor-in-2023/index.html

Ten years from Snowden revelations – what’s next for Tor and privacy online? | Tor Projecthttps://blog.torproject.org/tor-in-2023/Open linkView original on monero.town
16

Victory: Utah Supreme Court Upholds Right to Refuse to Tell Cops Your Passcode

NOTE: This is about the Fifth Amendment protection against self-incrimination after a search warrant for someone’s cell phone is procured; not about digital privacy in general at the U.S. Border (a warrantless search).

See also: https://monero.town/post/1134494 EFF to Supreme Court: Fifth Amendment Protects People from Being Forced to Enter or Hand Over Cell Phone Passcodes to the Police

Victory: Utah Supreme Court Upholds Right to Refuse to Tell Cops Your Passcodehttps://www.eff.org/deeplinks/2023/12/victory-utah-supreme-court-upholds-right-refuse-tell-cops-your-passcodeOpen linkView original on monero.town
68

Four more months of Section 702 snooping slipped into $890B US defense budget bill

Now before the House, HR 6570 proposes to reauthorize Section 702 for three years — but with reforms including requiring all US intelligence agencies to obtain a warrant before conducting a US person query.

a competing bill, the FISA Reform and Reauthorization Act of 2023 (HR 6611), doesn't include a warrant requirement — and, in fact, includes language that many worry could be used to force private US companies into assisting in government-directed surveillance

Four more months of Section 702 snooping slipped into $890B US defense budget billhttps://www.theregister.com/2023/12/14/congress_renews_fisa_section_702/Open linkView original on monero.town
6

After years of frustration, Republicans tackle FISA reform on House floor with two options

House Intelligence Committee bill would also expand the definition of an electronic communication service provider include a broader range of providers, including those who “provide hardware through which people communicate on the Internet.”

See also: Tell Congress: They Must Defeat HPSCI’s Horrific Surveillance Bill | EFF Action Center

After years of frustration, Republicans tackle FISA reform on House floor with two optionshttps://justthenews.com/government/congress/fisa-reform-bill-end-warrantless-searches-heads-house-floor-competing-separateOpen linkView original on monero.town
13
monero·MonerobySaki

Analysis of FinCEN Policy FINCEN-2023-0016: Overreach and Impact on Individual Rights — #jointheeclipse

How FinCEN May Be Violating Your Rights
A call to action against FINCEN proposal 2023-0016A
Written By Preston Pysh

Eroding Anonymity Through Additional Verification: The mandate for “Additional Customer Identity Verification Measures for Transactions Involving Unhosted Wallets” is a direct affront to privacy and anonymity. This requirement transgresses on the First Amendment’s sanctuary for anonymous speech

A Direct Assault on Anonymity-Enhanced Currencies: The “Prohibition on the Use of Anonymity-Enhanced Convertible Virtual Currencies (AECVC)” is nothing short of a legislative bulldozer through the edifice of privacy.

See also: Preston Pysh says proposed FinCEN crypto rules violate US Constitution

Analysis of FinCEN Policy FINCEN-2023-0016: Overreach and Impact on Individual Rights — #jointheeclipsehttps://egodeath.capital/blog/fincen-may-be-violating-your-rights-bitcoinOpen linkView original on monero.town
4

By 2030 EU wants to provide all citizens with a “European Digital Identity Wallet” to be used for online shopping and more

Bis zum Jahr 2030 will die EU allen Bürger:innen eine „European Digital Identity Wallet“ (ID-Wallet) zur Verfügung stellen. Sie soll on- wie offline bei Verwaltungsgängen und Bankgeschäften, aber auch bei Arztbesuchen, Alterskontrollen oder beim Internetshopping zum Einsatz kommen.

(By 2030, the EU wants to provide all citizens with a “European Digital Identity Wallet” (ID wallet). It is intended to be used online and offline for administrative procedures and banking as well as medical visits, age verification, and internet shopping.)

The article (in German) is mostly about eIDAS 45
Cf. https://monero.town/post/1018961 Last Chance to fix eIDAS: Secret EU law threatens Internet security

(There are many English articles about it; see e.g.
https://mullvad.net/en/blog/eu-digital-identity-framework-eidas-another-kind-of-chat-control )

Though not the main topic of the article, this “ID wallet” thing sounds disturbing. (EU politicians calls a normal wallet “unhosted wallet” and don’t like it very much.)

By 2030 EU wants to provide all citizens with a “European Digital Identity Wallet” to be used for online shopping and morehttps://netzpolitik.org/2023/eidas-reform-schlagabtausch-zwischen-forschenden-und-eu-parlament/Open linkView original on monero.town
8
meta·MetabySaki

Image Hosting Catbox Blocks Tor (Use Catbox normally, and Tor user can’t see your images): Solutions + How to embed 3rd party (clickable) images in general

On the front page of monero.town, sm.ms and catbox.moe are recommended as image hosting services. Unfortunately both are not Tor-friendly, esp. Catbox blocks Tor.

The Cock.li guy comes up with a solution.

  1. Solution about Catbox: Just change cat in the URL to fat and the image is viewable for Tor users!

Example https://monero.town/post/1025717 where
https://files.catbox.moe/6z3p3z.jpg is not viewable via Tor
https://files.fatbox.moe/6z3p3z.jpg would be viewable via Tor

  1. How to use an inline image (in general, not only Catbox)

The syntax is ![](URL) so…
![](https://files.fatbox.moe/6z3p3z.jpg)

Result:

  1. How to make it a Clickable thumbnail

Text link would be [Text](URL) you can replace Text with an inline image, URL with the image URL, i.e.
[![](URL)](URL) so…
[![](https://files.fatbox.moe/6z3p3z.jpg)](https://files.fatbox.moe/6z3p3z.jpg)
Result


Note: Optionally you can put Alt text in ![] as in
![Monero-chan is happy](https://sample.net/happy-monerochan.png)


Another hosting service imagebam.com is iffy but Tor friendly, easy to upload images there from Tor Browser & you can direct-link to the uploaded full image.

Using 3rd party image hosting services has privacy implications, but it will save the server resource of monero.town.

https://fatbox.moe/Open linkView original on monero.town
3

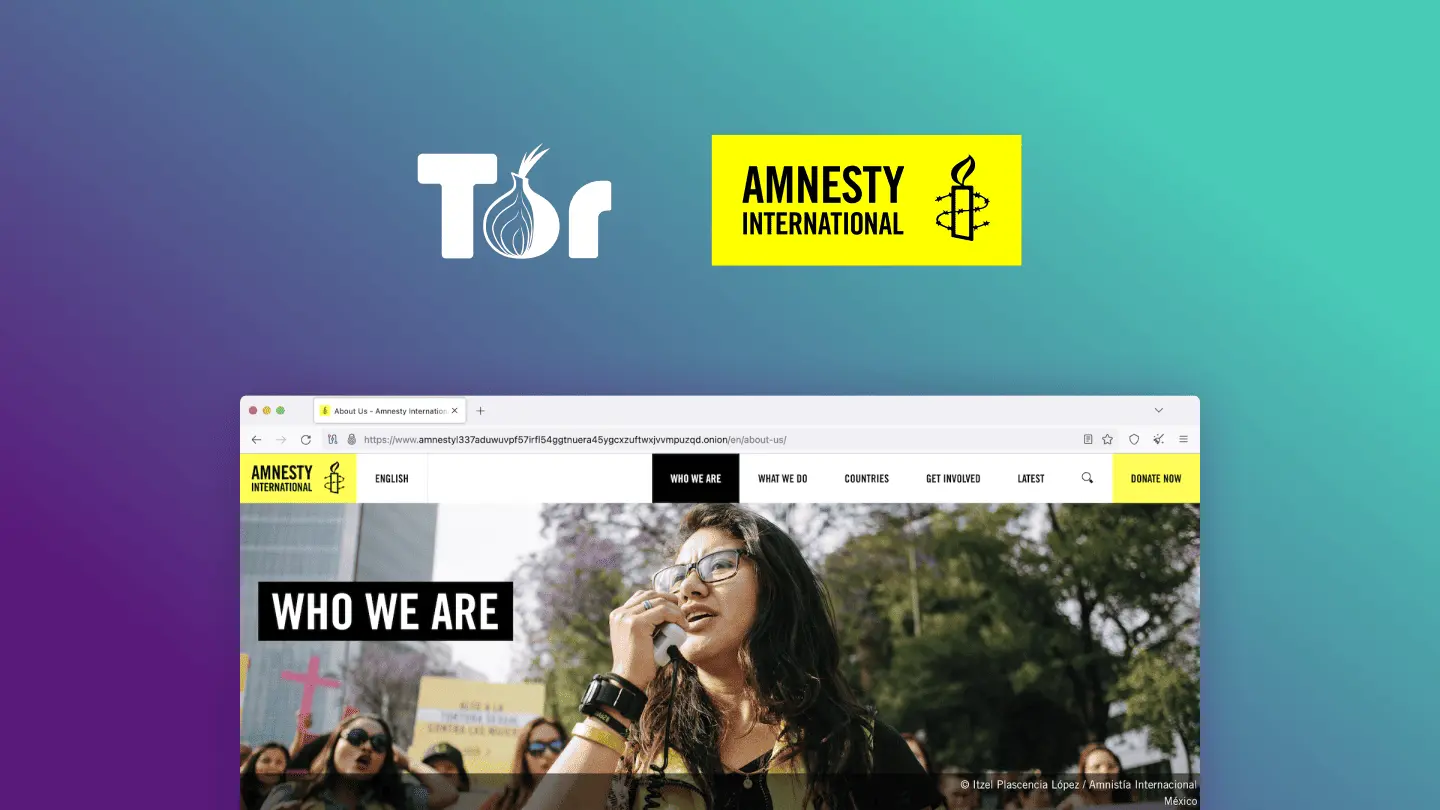
Amnesty International now available as .onion | Tor Project

Many countries use censorship systems to block access to human rights resources

.onion sites are particularly useful at maximizing internet users' privacy and anonymity because they never leave the Tor network.

While technically I2P might be better, it’s good news that a recognized human rights organization has adopted an onion, because that will improve the “shady” image of Tor, esp. hidden services (aka darknet), as in “privacy technology is good, not for criminals, but for you, for everyone. Using Tor is normal, and Monero is a great tool.”

Amnesty International now available as .onion | Tor Projecthttps://blog.torproject.org/amnesty-international-launches-onion-service/Open linkView original on monero.town
32
moneromining·Monero MiningbySaki

Nintendo Switch gets 230 hashes per second mining Monero

Apparently, the Nintendo Switch gets 230 hashes per second mining #Monero

Can you mine crypto with a Nintendo Switch? https://cryptonews.net/news/mining/27918548/

Interestingly, RandomX, the Monero mining algorithm, allows for alternative experiments like this due to being ASIC-resistant. Miners can use simple CPUs or gaming devices to run the algorithm and try their luck at block discovery while supporting network security.

https://nitter.oksocial.net/DontTraceMeBruh/status/1729488206863704136Open linkView original on monero.town
9

The French National Police is unlawfully using an Israeli facial recognition software [installed massively and secretly. The Minister ordered an investigation]

law enforcement has been using […] systems since 2015, in utmost secrecy. The software in question […] can track a person across a network of cameras, for instance, by the color of their sweater

Any policeman […] can request to use [it]

The potential use of facial recognition worries within the institution itself. […] In France, facial recognition is only authorized in rare exceptions

This massive installation was carried out outside the legal framework provided by a European directive and the French Data Protection Act

The National Commission on Informatics and Liberty (CNIL), a French administrative regulatory body, started an investigation against the French Minister of the Interior [1][2]. The Minister, Gérald Darmanin ordered an investigation [2].

La Cnil […] annonce l’ouverture d’une enquête contre le ministère de l’Intérieur. Elle soupçonne la police d’utiliser un logiciel de reconnaissance faciale, depuis 2015, en dehors de tout cadre légal. Qu’en est-il ?

(CNIL suspects the police are using facial recognition outside any legal framework. Comments? - Gérald Darmanin’s answer: The news is true. I ordered an investigation.)

https://disclose.ngo/en/article/the-french-national-police-is-unlawfully-using-an-israeli-facial-recognition-softwareOpen linkView original on monero.town
16

Secretive White House Surveillance Program Gives Cops Access to Trillions of US Phone Records

the White House has, for the past decade, provided more than $6 million to the program, which allows the targeting of the records of any calls that use AT&T’s infrastructure

the program takes advantage of numerous “loopholes” in federal privacy law

the DAS program has been used to produce location information on criminal suspects and their known associates, a practice deemed unconstitutional without a warrant

(This website is a bit annoying.)

Secretive White House Surveillance Program Gives Cops Access to Trillions of US Phone Recordshttps://www.wired.com/story/hemisphere-das-white-house-surveillance-trillions-us-call-records/Open linkView original on monero.town
22

Cock.li is back open for public registration (Onion-capable free email provider)

See https://monero.town/post/968066

Onion http://rurcblzhmdk22kttfkel2zduhyu3r6to7knyc7wiorzrx5gw4c3lftad.onion/

This free email provider is not for everyone. Sometimes a Cockmail address is not accepted to register something. Sometimes, though not often, another email provider may indiscriminately block email from Cock.li. Afaik Cock.li<->Proton, Cock.li<->Tuta work.


PS: Admin, Vincent Canfield @[email protected]

http://rurcblzhmdk22kttfkel2zduhyu3r6to7knyc7wiorzrx5gw4c3lftad.onion/Open linkView original on monero.town
10
meta·MetabySaki

Should we remove this Buskill ad? (Got 4 reports against it)

https://monero.town/post/1144305

Bicoin Black Friday: BusKill (Open-Source Hardware Dead Man Switch) Announces 10% Discount

There are 4 reports saying this is spam, and it is indeed cross-posting link spam, and feels slightly excessive but not extremely so (?).

The thing is, Monero.town doesn’t forbid ads, and freedom of speech is important even if what is said is unpleasant for me or for someone else. Thoughts?


Edit: Since someone has appointed me as a mod in !privacy, where https://monero.town/post/1144305 is, I can remove it, except I don’t want to remove anything unless really necessary. The lack of guidelines about ads in monero.town means, the OP didn’t do anything against the rule(s).

I couldn’t remove the new one in !moneromarket https://monero.town/post/1142415 Not sure if @[email protected] thinks it’s bad enough, either. Monero is censorship-resistant, meaning we tend to hate deleting someone else’s speech/expression just because it’s subjectively disagreeable.


Given that Monero is money after all and some for-profit services are useful for its users too, probably commercial posts (ads) should be allowed in general, if not excessive. And BusKill ads are not excessive in terms of frequency, like only once a month.

Perceived link spamming (self-promotion) advertising SimplifiedPrivacy has been also noticed by many including myself, which has been like once or twice a week, and explicitly questioned here ( https://monero.town/post/1085883 ); but many (including myself) think these posts can be useful nevertheless, the poster being knowledgeable.

View original on monero.town
2

Children's tablet has malware and exposes kids' data, researcher finds [and she installed Tor 🧅 to protect her daughter’s anonymity]

The app store “collects and sends data […] This includes information like device model, brand, country, timezone, screen size, view events, click events, logtime of events, and a unique KID ID,”

Hancock didn’t return the tablet to her daughter until after making changes to protect her daughter’s privacy.

[She] even installed Tor, a browser that is designed to protect the anonymity of its user.

An awesome Mom, like Mrs. Roberts from xkcd!

Children's tablet has malware and exposes kids' data, researcher finds [and she installed Tor 🧅 to protect her daughter’s anonymity]https://techcrunch.com/2023/11/16/childrens-tablet-has-malware-and-exposes-kids-data-researcher-finds/Open linkView original on monero.town
8
monero·MonerobySaki

"Monero on the front page of The Economic Times in India” [Is someone crowdfunding a Monero ad in India’s economic newspaper?] (Don’t take this too seriously)

EDIT: Don’t take this too seriously; do not actually send a donation (unless you really want to, like admiring “Nice photoshopping!” “Thanks for the fun pic”). While it’s entertaining and thought-provoking, using their work this way is ethically questionable too. As @z0rg0n pointed out, one could even see this as a scam. Although it’s a fine work and freedom of expression is more important, this may more properly belong to “Memes”.


EDIT2: This post and “cool if real” by @alphonse https://monero.town/post/1122495 were created almost at the same time. That was a coincidental post conflict; @alphonse’s post was actually earlier by about 1 hour!


Is someone crowdfunding a Monero ad in India’s economic newspaper?

Interestingly, a Monero ad could be circulating in India’s traditional English newspaper: The Economic Times. The pseudonymous Stoic, author of “The Monero Standard,” shared a picture of the newspaper’s November 16th edition. In the picture, it is possible to see the paper’s opened front page with a large ad about XMR.

“Monero transactions respect your privacy. Can you say that about the INDIAN RUPEE or the U.S. DOLLAR?”

Moreover, the image also includes a QR-Code for donations in “XMR only,” which suggests its owner is expecting to crowdfund what was spent for this supposed insertion.

https://nitter.oksocial.net/TheStoicCoiner/status/1725132861404254341Open linkView original on monero.town
1